;}%3c/style%3e%3cradialGradient%20id='b'%20cx='256'%20cy='256'%20fx='256'%20fy='256'%20r='189.71'%20gradientUnits='userSpaceOnUse'%3e%3cstop%20offset='0'%20stop-color='%2319f0a6'%3e%3c/stop%3e%3cstop%20offset='1'%20stop-color='%231bda94'%3e%3c/stop%3e%3c/radialGradient%3e%3c/defs%3e%3cpath%20class='c'%20d='M257.16,452.01c-2.88,0-5.75-.75-8.33-2.24-108.93-63.17-150.31-153.71-165.84-218.55-16.79-70.08-7.87-124.95-7.49-127.25.93-5.5,4.56-10.17,9.66-12.43,1.66-.73,41.34-18.04,103.49-26.76,57.21-8.03,145.25-9.96,239.73,26.46,5.22,2.01,9.07,6.52,10.25,11.98,1.18,5.47-.47,11.16-4.4,15.15l-174.54,177.26c-3.1,3.15-7.34,4.93-11.76,4.95h-.06c-4.4,0-8.62-1.75-11.73-4.86l-56.04-56.04c-6.48-6.48-6.48-16.99,0-23.47,6.48-6.48,16.99-6.48,23.47,0l44.21,44.21,144.46-146.71c-134.71-42.84-252.87-6.82-285.07,4.87-1.59,17.46-3.29,58.23,8.4,106.19,19.87,81.5,67.48,145.82,141.57,191.32,108.55-66.71,141-163.02,148.95-232.91,1.03-9.11,9.25-15.66,18.37-14.61,9.11,1.04,15.65,9.26,14.61,18.37-9.01,79.2-46.44,189.1-173.6,262.84-2.57,1.49-5.45,2.24-8.33,2.24Z'%3e%3c/path%3e%3c/svg%3e) DRIMT
Built from the trenches of digital risk.
Drimt was born from years of running a digital company and helping organizations tame logs, data and compliance — across fintech, banking, public institutions and ecommerce.
The problem we lived
For years we operated a digital agency and platform business that served regulated and high-stakes customers. Every project surfaced the same pain: fragmented logs, scattered evidence, inconsistent controls and audit cycles that drained engineering teams.
We saw teams reinvent the same spreadsheets for NIS2, DORA, ISO 27001 and SOC 2 — losing weeks per audit and months per incident. There had to be a better way.
Industries that shaped us
- Fintech
- Banking
- Public sector
- Ecommerce
- Startups
- NIS2 industries
Each of these worlds taught us something different about risk, evidence and accountability — and Drimt is the product we wished existed back then.
People behind Drimt
Thibault Debatty
CEO · Director of the Cyber Defence Lab
Thibault brings deep expertise in cyber defence research, detection engineering and threat intelligence.
Daniel Sum
CPTO · Chief Product & Technology Officer
Daniel leads product and technology at Drimt, drawing on years of building and operating digital platforms for regulated industries.
Zineb Gridda
Freelance Consultant · CISO-as-a-Service · IT & Audit Trainer
Zineb advises organizations on IT audit, GRC, NIS2, DORA and ISO 27001, backed by 16+ years across regulated industries.
Yassine El-Jakani
Freelance Consultant · DevSecOps & Cloud Security
Yassine brings hands-on DevSecOps, cloud security and security automation expertise across OCI, Kubernetes and secure software delivery.
Guided by industry leaders
Senior cyber defence and information security leaders advising Drimt on strategy, resilience and compliance.
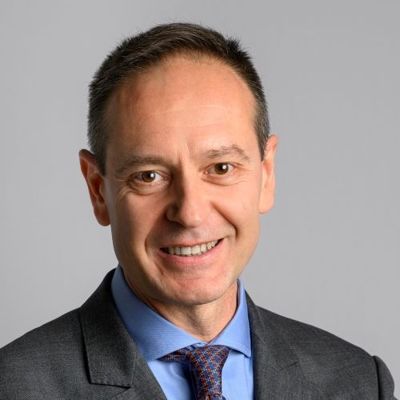
Philippe Pacom
Director of Cyber Defence Operations · La Poste Groupe
20+ years in IT and cybersecurity. Former ANSSI strategic operations lead for elections, Rugby World Cup and the Olympic & Paralympic Games.
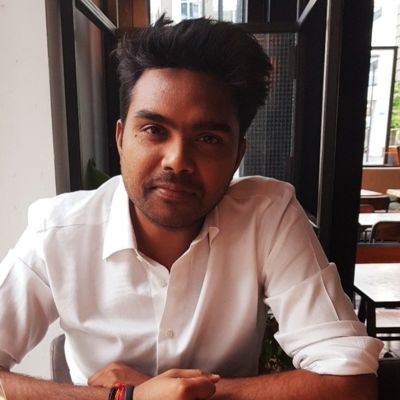
Alok Pandey
Head of Information Security Governance · ABN AMRO (ICS)
Leads information security governance at International Card Services, a 100% subsidiary of ABN AMRO. 15+ years across risk management, SOC, network defence, pentesting and program leadership — NIST, GDPR, SOC 2 and ISO 27001.
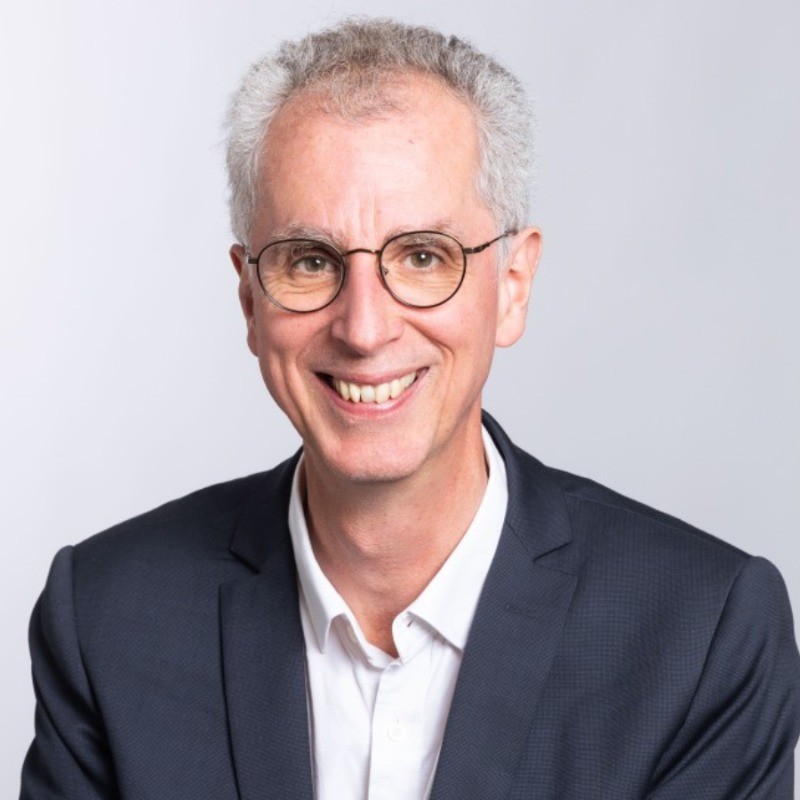
Jean-Benoit Pimpaneau
Group CIO · RATP Dev
29+ years in IT leadership, currently Group CIO at RATP Dev — driving IT transformation, enterprise architecture, cybersecurity and risk management for a global transport group.
Where teams get value
Three situations where Drimt turns scattered compliance and security work into a clear, prioritized plan.
Compliance readiness
Facing ISO 27001, NIS2 or the EU AI Act? Map every requirement to a concrete action, see exactly what is missing and who owns it, and stop guessing what the auditor will ask.
Supply-chain protection
Your code is only as safe as what you depend on. Drimt watches your repositories and dependencies, surfaces attack paths early and ranks the fixes that actually reduce risk.
Board & audit reporting
Pull evidence out of spreadsheets and tickets. Get risk reporting your leadership understands and your auditors can work with — ready to share in minutes, not weeks.
Reach out to Drimt
Tell us about your compliance, risk or audit challenges — we read every message.
Get in touch
Questions, contact requests or partnerships — drop us a line.